

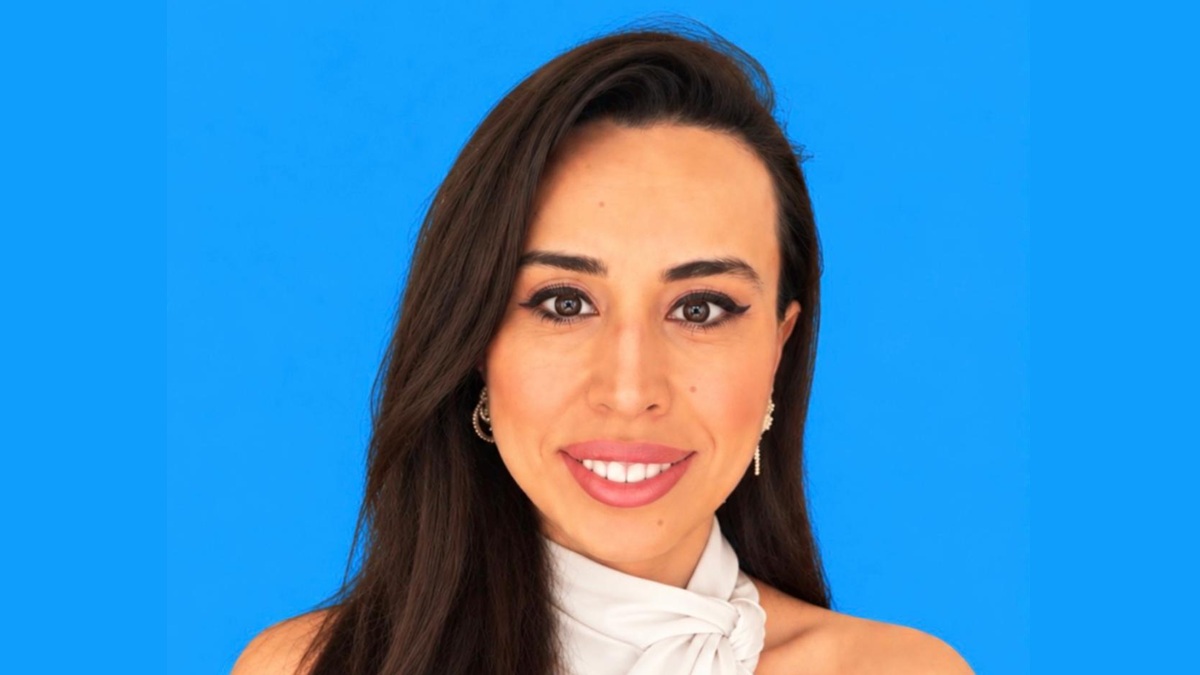
Nur Sevis, CEO, ThreatMon, discusses the evolving cyber threat landscape, the growing role of AI in cyberattacks, dark web intelligence and how enterprises can strengthen proactive threat detection and response.
How would you describe the current cybersecurity landscape for enterprises, and which risks are rising fastest as attackers increasingly adopt AI, automation and ransomware-as-a-service?
The cybersecurity landscape has become increasingly industrialised. Attackers now operate like a supply chain, with one group stealing credentials through infostealer malware, another selling the compromised access, and ransomware-as-a-service affiliates monetising it. Each stage has become cheaper and faster than it was even two years ago.
AI has accelerated this trend further. Phishing emails are now fluent in virtually any language, deepfake voices are being used to pressure finance teams, and automated scanners can identify and weaponise newly disclosed vulnerabilities within days, sometimes hours.
The fastest-rising risks we see are identity-based. These include stolen session cookies and tokens that bypass multi-factor authentication (MFA), exposed API keys in public code repositories, and compromised third-party access through suppliers and agencies. The common thread is that breaches often begin outside the traditional enterprise perimeter, in areas that security teams may not be monitoring.
Which advanced threats should CIOs and CISOs in the Middle East and Africa be most concerned about over the next 12 to 24 months, and why are so many organisations still caught off guard?
Three threats stand out for the region. First, ransomware and data extortion targeting the finance, energy, government and healthcare sectors, where rapid digitalisation has expanded the attack surface faster than security teams have grown. Second, state-aligned and hacktivist activity, which tends to increase around geopolitical events and frequently targets critical infrastructure and operational technology (OT) environments. Third, large-scale fraud and brand impersonation, ranging from fake banking applications to cloned government portals, which exploit the region’s high mobile adoption.
Organisations are often caught off guard because their visibility stops at the network edge. Early warning signs, such as leaked employee credentials, newly registered lookalike domains or access brokers advertising VPN logins, frequently appear on the dark web and open internet long before an alert reaches the security operations centre (SOC). If organisations are not monitoring these sources, the first indication of a breach may be a ransom note.
What role does the dark web play in the modern attack chain, from leaked credentials and initial access sales to ransomware leak sites? How early can organisations realistically detect that they are being targeted?
The dark web is the marketplace connecting every stage of the attack chain. Infostealer logs containing corporate credentials and session cookies are sold in bulk. Initial access brokers advertise VPN, Remote Desktop Protocol (RDP) or cloud console access to specific companies, often identifying their sector, country and revenue. Ransomware affiliates purchase this access, while leak sites are subsequently used to pressure victims.
This creates an important detection window. Between the theft of a credential and its eventual use, there can often be several weeks. In cases we have observed, this period can extend to two months.
With continuous monitoring of stealer logs, forums, Telegram channels and access listings, organisations can realistically identify targeting attempts before an intrusion occurs. They can then reset compromised credentials, revoke active sessions and close access points while remediation is still relatively straightforward and inexpensive.
What trends are you observing on underground forums and marketplaces that enterprises should be aware of, particularly concerning stolen data, access brokers, fraud and brand impersonation?
Several trends are becoming increasingly clear. Infostealer logs have emerged as a primary form of currency in cybercrime markets. A single infected personal laptop can expose corporate single sign-on (SSO), email and cloud credentials simultaneously. Many infections originate from cracked software and pirated games, meaning the risk can begin at home rather than within the corporate environment.
Access brokers are becoming more specialised, selling access to organisations in specific sectors and countries, including banks, telecommunications companies and government bodies across the Middle East and Africa. Cybercriminal communities are also shifting from traditional forums to Telegram and private channels, making them harder to monitor without dedicated intelligence collection.
On the fraud front, we are seeing phishing kits sold through subscription-based services, fake mobile applications, and the impersonation of executives and brands across social media. Third parties are also becoming a growing source of data exposure, with agencies, developers and suppliers inadvertently exposing customer information, access tokens or source code in public repositories and other online locations.
ThreatMon combines attack surface intelligence, dark web monitoring, fraud protection and cyber threat intelligence in a single platform. How does this unified approach help security leaders move from reactive defence to proactive protection?
Attackers do not think in product categories, so defenders should not either. A single attack can involve an exposed asset, a leaked credential and a fraudulent domain. When these elements are monitored through separate tools, security teams may fail to connect the dots.
ThreatMon brings attack surface intelligence, dark web monitoring, fraud and brand protection, supply chain risk and cyber threat intelligence together in one platform, providing a shared view of an organisation’s digital footprint.
For example, we can identify that a credential leaked on an underground forum belongs to an employee who has access to an internet-facing system that we have already flagged as vulnerable. This enables security teams to understand the combined risk and prioritise remediation accordingly.
Our Hacker Insight capability allows organisations to view their digital presence from an attacker’s perspective. This makes proactive protection more practical, enabling teams to address exposures, reset compromised credentials and take down fraudulent websites before they are exploited.
Many CISOs are overwhelmed by data and security alerts. How does ThreatMon transform raw intelligence into actionable insights, and what role do AI and machine learning play in this process?
CISOs do not need more data; they need a reliable measure of risk that they can act upon. This is the journey ThreatMon is designed to support, moving organisations from raw data to meaningful risk scores.
We begin with the customer’s own assets, domains, brands, executives and suppliers, collecting intelligence from the open web, dark web, Telegram channels and stealer logs. AI and machine learning then correlate these signals, eliminate duplicates and false positives, and assess each finding based on its exploitability, exposure and potential business impact.
Brainify AI translates these findings into a clear risk score for the organisation, its assets and its suppliers. It also explains what has changed, why it matters and what actions should be taken next. Every critical alert is validated by our 24/7 analyst team.
Instead of receiving thousands of raw indicators, CISOs get a prioritised list of actions and a risk score that improves as vulnerabilities and exposures are addressed.
How does ThreatMon integrate with existing security tools, including SIEM, SOC workflows and incident response processes, to ensure intelligence leads to faster detection and response?
Intelligence creates value only when it reaches the people and tools responsible for taking action. ThreatMon provides APIs and ready-made integrations that allow alerts and indicators to flow directly into the solutions customers already use.
These include SIEM and XDR platforms such as Splunk, IBM QRadar, Microsoft Sentinel and Cortex XSIAM; SOAR solutions such as Cortex XSOAR; security tools from CrowdStrike, Palo Alto Networks and Fortinet; and ticketing platforms such as ServiceNow and Jira.
Indicators of compromise (IOCs) can automatically enrich security detections, while alerts relating to leaked credentials or exposed assets can trigger ticket creation. For incident response, analysts can investigate threats within the platform using big data search across our collections, phishing investigation and malware analysis capabilities. They can also request the takedown of malicious domains, fake applications and fraudulent social media accounts with a single click.
Our objective is to eliminate the need for teams to constantly switch between tools. Intelligence should reach security professionals within their existing workflows, accompanied by the context they need to respond in minutes rather than days.
What advice would you give CIOs and CISOs looking to strengthen their threat readiness, and how can they demonstrate the return on investment in threat intelligence to their boards?
First, understand what attackers can see. Organisations should map their external attack surface and supplier connections while working on the assumption that some credentials may already be compromised.
Second, be cautious about the temptation to build threat intelligence capabilities internally. With AI, a small team can now develop a monitoring tool in a matter of weeks. However, threat intelligence is not a static product. Intelligence sources disappear, attackers continuously change their tactics, and monitoring tools require constant updates and maintenance.
A year later, the employees who developed the tool may find themselves spending most of their time maintaining data collectors. What initially appeared to be a cost-saving exercise can eventually become a permanent staffing expense. Organisations should keep their security teams focused on threat analysis and response rather than maintaining intelligence collection infrastructure.
When demonstrating ROI to the board, organisations should focus on measurable outcomes rather than the volume of intelligence collected. These include exposures closed before exploitation, time taken to remediate vulnerabilities, fraudulent domains taken down and improvements in the organisation’s overall risk score. A consistently declining risk score is a meaningful indicator of progress that every board can understand.