

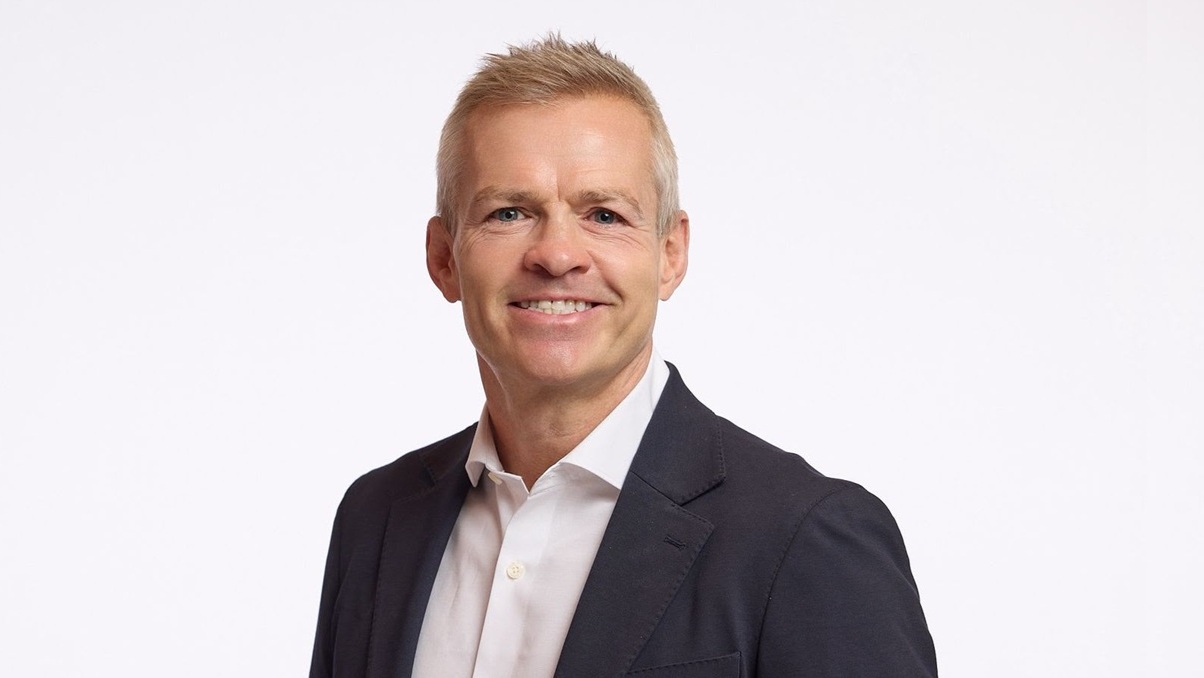
John Brown, Regional Director for Middle East & Africa at HackerOne, says the company’s MEA growth will be driven by sovereign alignment, trusted regional partners, and a continuous‑security model built for fast‑digitising economies.
What strategic priorities come with your appointment as Regional Director, and how do you plan to shape HackerOne’s footprint across the Middle East’s rapidly evolving cybersecurity landscape?
I’ve worked in this region for nearly 15 years, and the current momentum is unlike anything I’ve seen before. Saudi Arabia’s HUMAIN has signed $23 billion in AI infrastructure agreements with Nvidia, AMD, AWS, and Qualcomm. The UAE AI Strategy 2031 is being implemented, and PwC estimates that AI could contribute more than $320 billion to the Middle East economy by 2030. These developments present a significant opportunity for the cybersecurity community.
My first priority is to build on HackerOne’s existing foundation. We already work with more than 40 enterprise and government customers across MEA, and my role is to expand those relationships while deepening the value we provide.
That commitment is also reflected in our leadership. Our VP of EMEA and APAC, Vlad Nisic, recently relocated permanently to Dubai. As he put it: “This region continues to scale at a phenomenal pace and is less than seven hours from 70% of the global populace. It made perfect sense for me to relocate from London to Dubai in order to address all areas and to commit to the international market.” Having senior leadership based here means we can stay close to our customers and respond more directly to the needs of the region.
My second priority is to pursue a government‑aligned, partner‑led approach. Success in this market depends on working effectively with sovereign entities, developing the right channel relationships, and earning trust over time. I’ve built these kinds of programmes before at Darktrace, LogRhythm, and AttackIQ. HackerOne also has a strong partner base in Mannai, Green Method, and Saudi Southern, which gives us a solid platform for growth.
The third priority is to broaden the product conversation. Customers are no longer simply asking whether they need a bug bounty programme. They want to know how to manage continuous threat exposure across code, cloud, and AI systems at the pace required by today’s threat environment. That is increasingly a board‑level discussion. HackerOne helps close the loop from discovery and validation through to prioritisation and remediation.
What gives me particular confidence in the road ahead is that one of the Middle East’s leading banks is set to join our Customer Advisory Board. That matters because the board is not simply a collection of customer logos; it gives enterprise customers a direct role in shaping how the platform develops. Having a major regional bank involved means the realities of this market—including regulatory complexity, rapid AI adoption, digital transformation, and sovereign security—will be represented in HackerOne’s product direction.
We are not simply selling into MEA; we are building with the region.
How is HackerOne’s CTEM platform, combined with Hai’s agentic AI orchestration, transforming how Middle East enterprises discover, validate, and remediate vulnerabilities?
The practical change is a move away from relying mainly on scheduled assessments towards managing exposure continuously. Most organisations are not short of findings. The harder part is understanding which vulnerabilities are exploitable, deciding what to address first, and giving engineering teams enough context to fix them. CTEM brings discovery, validation, prioritisation, and remediation into one ongoing process.
Hai acts as the agentic orchestration layer across that process. It coordinates specialized AI agents across validation, prioritization, and remediation, helping teams reduce manual work, cut through noise, and move findings towards resolution faster. The goal is to connect each stage of exposure management so security and engineering teams can focus their time on the risks that matter most.
In our conversations with organisations across the Middle East, a recurring concern is how to adopt cloud, AI, IoT, and other new technologies without creating an unmanageable security workload. Periodic testing can leave gaps as systems and threats change between assessment cycles.
That is where the discovery‑remediation gap becomes important. Organisations are finding more vulnerabilities, but their capacity to fix them is not growing at the same rate. According to H1 Platform data, the resolution rate for critical‑severity findings has fallen significantly over the last year, even as critical‑finding mean time to remediate improved by more than 50%. The result is that the backlog of unresolved critical issues has grown 29x over that same timeframe.
For those delivering programmes linked to Vision 2030 or the UAE AI Strategy, the H1 Platform can help direct limited resources towards the exposures most likely to affect operations and reduce the time between finding a vulnerability and resolving it.
With AI red teaming and agentic pentesting becoming critical, how is HackerOne helping regional organisations secure frontier AI systems aligned with OWASP LLM Top 10, MITRE ATLAS, and NIST AI RMF?
Few areas of cybersecurity have changed as quickly as AI security. Not long ago, organisations were still deciding whether they needed AI red teaming. The conversation has since moved on to how testing can produce findings that are useful not only to security teams, but also to governance teams, boards, and regulators.
HackerOne tests the different layers of an AI system, including model behaviour, APIs, integrations, and agent workflows. Human security researchers guide and validate AI agent testing across those components to identify how they could be manipulated or misused.
The findings are mapped to established guidance from OWASP, MITRE, and NIST. This matters because many organisations already have detailed technical reports; the difficulty is translating those reports into evidence that supports governance and compliance. HackerOne’s validated findings include the exploitation technique, weakness classification, and relevant framework mapping, giving security and governance teams a common view of the risk.
We also have Agentic Pentest‑as‑a‑Service, which applies this approach continuously rather than through a single assessment. It uses AI to test and validate exploitability at scale while keeping human expertise and oversight at the centre of the process.
For organisations across the GCC deploying AI as part of national digital programmes, the practical requirement is clear: they need to demonstrate how systems have been tested, what was found, and what has been addressed. Framework‑aligned testing makes that evidence easier to produce and act on.
HackerOne reports a 210% rise in AI vulnerability submissions globally. What patterns or threat behaviours are you seeing specifically across Middle East enterprises adopting AI at scale?
Whilst that 210% increase is global, the patterns behind it are particularly relevant to the Middle East because local organisations are deploying AI quickly and at significant scale.
Prompt injection is the clearest example. Valid reports on our platform rose by 540%. In practical terms, an attacker manipulates an AI system into ignoring its instructions, potentially exposing data, bypassing controls, or taking actions outside its intended role. That becomes a serious concern when AI is being used in government services, banking, retail, and other customer‑facing applications.
We are also seeing more sensitive data exposure, access‑control failures, misconfigurations, and logic flaws. These weaknesses are often difficult to identify through automated scanning because the system may be working as designed at a technical level while still behaving in an unsafe way. Finding them requires people who understand how to test the system’s logic, supported by AI tools that can operate at scale.
AI is also accelerating both attack and defence. Attackers can use it to test more systems and explore weaknesses faster, so security teams need similar capabilities to keep pace. The important question is not whether AI is being used, but whether organisations can validate its behaviour continuously as applications and models change.
In my conversations across the region, the risk is increasingly discussed in terms of service disruption as well as data loss. Smart cities, transport networks, energy infrastructure, and public services all connect digital systems with the physical world. A vulnerability in those environments can have operational and, potentially, national security implications.
For organisations adopting AI at speed, periodic testing will not provide enough visibility. They need continuous testing, validated findings, and a clear process for getting the most significant issues fixed quickly.
What does HackerOne’s roadmap for the Middle East look like in 2026–27?
The focus for 2026–27 is to deepen our presence rather than simply expand our footprint. We already have established customers, regional partners, and senior leadership based in Dubai.
The next step is to become more closely involved in how organisations across the region manage cyber risk.
Partnerships will be central to that. In my experience, customers here place considerable value on local relationships, market knowledge, and long‑term commitment. Our partners bring that credibility, as well as an understanding of local compliance requirements and sovereign organisations. We will invest in helping them deliver the full CTEM offering, from validation and remediation to AI red teaming, while building the services capability needed to address customers’ growing remediation backlogs.
For enterprise customers, the aim is to move the conversation beyond individual programmes or assessments. We want to help them establish a continuous process for identifying, validating, and resolving exposure across code, cloud, and AI systems.
Government and critical infrastructure will also be a major area of focus. Bodies such as SAMA, Saudi Arabia’s NCA, the UAE NCSC, and Qatar’s NCSA are placing greater emphasis on vulnerability management, ongoing assurance, and secure AI adoption. HackerOne can help organisations meet those expectations with evidence of what has been tested, what is exploitable, and what has been fixed.
We also want to create more opportunities for regional security researchers to contribute to HackerOne’s global community. Growing participation across the Middle East brings more diverse perspectives, local knowledge, and attacker creativity into the security process, while giving organisations access to expertise that automation alone cannot replicate.
By the end of next year, progress should be visible in stronger partners, broader enterprise adoption, more regional researchers, and deeper engagement with government and critical infrastructure.
How is customer feedback from Middle East organisations shaping HackerOne’s product evolution?
The most consistent message from customers in the region is that they do not need another source of findings. They need help deciding what matters and getting it fixed.
That feedback is reflected in H1 Validation. As submission volumes grow, security teams cannot review everything manually or keep adding headcount. H1 Validation combines agentic AI with human expertise to filter out noise and return findings that are both credible and actionable.
Customers have also been clear that validation is only part of the process. A confirmed vulnerability still creates work if the engineering team receives a generic report that does not fit its tools or codebase. H1 Remediation addresses that by producing developer‑ready fix plans grounded in the customer’s source code and delivering them through the tools engineers already use. Remediation times may be improving, but critical backlogs continue to grow. The friction between identifying an issue and fixing it remains a major constraint.
AI security is another recurring theme in my conversations here. Organisations across the GCC are adopting AI quickly, but many existing security processes were not designed to test models and agentic systems. Customers want findings that technical teams can act on and governance teams can use. Mapping AI red‑teaming results to the relevant OWASP, MITRE, and NIST frameworks helps meet both needs.
The result is a product roadmap increasingly focused on continuous testing, higher‑confidence validation, and a shorter path from finding to fix. Greater regional representation on our Customer Advisory Board will make that feedback loop even more direct.
Q7: What innovations, demos, and AI‑security capabilities will HackerOne showcase at GISEC 2026?
The message we are bringing to GISEC is that most CISOs are not short of findings. The challenge is establishing which ones are exploitable and getting them fixed quickly.
We’re here to demonstrate how the H1 Platform connects that process in one continuous workflow. Visitors will see Hai analyse and contextualise exposure, H1 Validation separate credible risk from noise, and H1 Remediation turn validated findings into developer‑ready fix plans. The focus will be on showing how the technology works in practice, rather than relying on product slides.
AI security will be a major part of the demonstration. We will show how HackerOne tests models, APIs, integrations, and agent workflows, and how it maps validated findings to the relevant OWASP, MITRE, and NIST frameworks. For CISOs, that means technical results their teams can act on and evidence they can use in board and regulatory discussions.
For partners and hyperscalers, we will also discuss how our work with OpenAI, CrowdStrike’s Project Quiltworks, and Anthropic’s Project Glasswing is bringing frontier AI into security workflows. The practical value is faster triage, stronger exploitability validation, and clearer remediation guidance at enterprise scale.
Our data shows that vulnerability submissions are rising while unresolved critical issues continue to accumulate. Adding another scanner will not resolve that on its own. Organisations need to connect discovery, validation, and remediation so that findings move through to a shipped fix. That is what we want customers and partners to see for themselves at GISEC.