


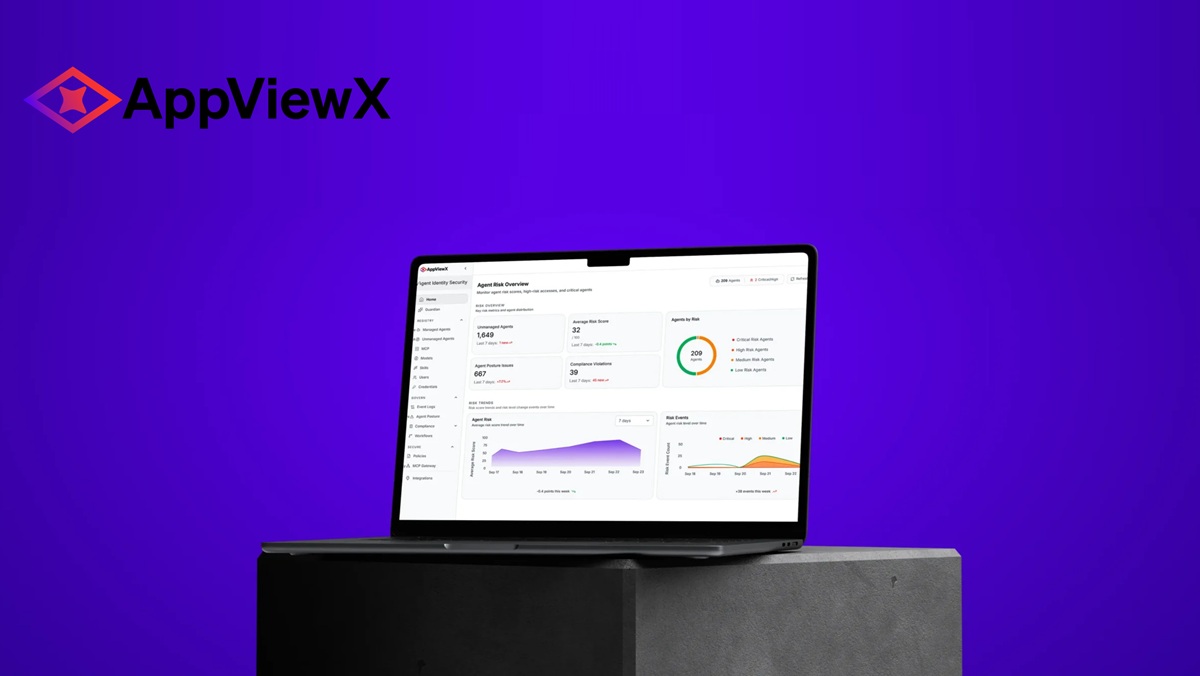
AppViewX expanded Agent Identity Security capabilities, a solution that lets enterprises discover every agent, sanctioned or shadow; govern their posture and maintain audit-ready activity logs; and monitor and control every agent action in real time. AppViewX now also issues quantum-resilient agent identities, so trust in every agent holds as the cryptography infrastructure layer of the enterprise evolves.
The sprawl of AI agents is creating a new identity challenge for CISOs. Each agent brings models, credentials, privileges, skills and connections to enterprise systems that must be secured, and agents can be created and act autonomously or on behalf of humans at a pace traditional access controls were never built to handle. The credentials and cryptography that establish trust in those identities must also remain secure as enterprises prepare for a post-quantum world.
AppViewX approaches agent security as an identity and access problem, but one that requires a new paradigm. Rather than simply retrofitting traditional human identity architectures, Agent Identity Security is purpose-built at the identity layer. It offers the industry’s most comprehensive discovery, governance, and runtime security capabilities for coding agents, enterprise productivity agents, SaaS agents, and custom-built agents.
The latest Agent Identity Security capabilities help enterprises:
Discover every agent, including Shadow AI, with an expanded AI Bill of Materials:
AppViewX discovers sanctioned and unsanctioned agents across the enterprise, with new capabilities to discover browser-based and short-lived, script-based shadow agents. The AI Bill of Materials (AIBOM), which gives security teams a centralized view of every agent’s models, MCP tools, credentials, and identities, now extends to the skills agents can access, so that teams can assess what these skills enable and flag unsafe capabilities. Unlike alternative solutions that rely on a single detection method, AppViewX combines its own new lightweight endpoint Guardian Agent with API integrations across EDR, SaaS, and cloud platforms, giving security teams confidence that no shadow agent goes undetected.
Govern every MCP server, including shadow servers, with a new MCP Gateway:
AppViewX discovers sanctioned and shadow MCP servers and continuously assesses their risk and posture. Just-in-time access eliminates standing privileges, granting agents access to MCP servers and tools only when and for as long as needed, based on identity and agent context. Sensitive data is redacted using built-in controls or by integrating with existing data security tools such as Microsoft Purview.
Stop any agent at runtime with the new Agent Kill Switch:
AppViewX offers the industry’s most comprehensive approach to terminating an agent and its active sessions, whether automatically when triggered by events, through runtime policies, or on demand. Security teams can easily build event-driven workflows that terminate an agent based on changes AppViewX detects, such as configuration changes. Through integration with the Shared Signals Framework (SSF), workflows can also act on signals from third-party security tools. Agents can also be stopped leveraging runtime policies based on resource type, the agent itself, and its intent, or on demand from the console. Unlike alternative approaches, the Agent Kill Switch covers both sanctioned and shadow agents and does not depend on an MCP gateway.
Govern AI programs with expanded cost and compliance controls:
AppViewX now shows AI token usage, trends, and costs, and lets enterprises set threshold policies to prevent runaway spending. To help enterprises keep pace with emerging AI regulations, AppViewX now enables organizations to assess and demonstrate alignment of their agent deployments against the OWASP Top 10 for Agentic Applications and Agentic Skills, MITRE ATLAS, GDPR, HIPAA, ISO 27001/42001, and NIST SP 800-53 Rev. 5, alongside NIST AI RMF, the EU AI Act, SOC 2, and SEC Cyber Disclosure.
This release of Agent Identity Security is the latest proof point of AppViewX’s broader vision for securing identity, credentials, and cryptography together, for agents and machines.
As enterprises deploy AI agents, each one becomes a unique identity class that needs credentials to reach APIs, tools, and other agents, often at a scale and speed traditional processes can’t manage. OAuth governs what an agent may do on a user’s behalf, but the agent must still prove who it is, and static identities are easy to leak and hard to manage at agent scale.
AppViewX has extended its core PKI (Public Key Infrastructure) and CLM (Certificate Lifecycle Management) platform capabilities to issue and cryptographically verifiable quantum-resilient agent identities, which adds an additional trust layer when authenticating via an Enterprise IdP. Since these identities chain to the customer’s AppViewX-managed PKI, security teams get one trusted root, a clear tamper-evident audit trail, and a single place to build quantum resilient agent identities.